A Third Signal for Digital Identity
Most digital identity systems are very good at answering a particular question: does this actor control the required credential?
A private key can answer that extremely well. Multi-signature schemes can require several independently controlled keys, while zero-knowledge proofs can establish particular claims without exposing the underlying information. Those are powerful tools, but they don't answer every question we sometimes smuggle into the word identity.
A valid signature tells us that the signing operation had access to a private key. Depending on the surrounding system, that may provide very strong evidence about authorization. It doesn't independently tell us whether the person using the key is behaving normally, whether they're under coercion, whether an organization still resembles the organization that originally established its credentials, or whether something important has changed since the credential was issued. None of this means the key failed. The key did its job. We're asking it a question it wasn't designed to answer.
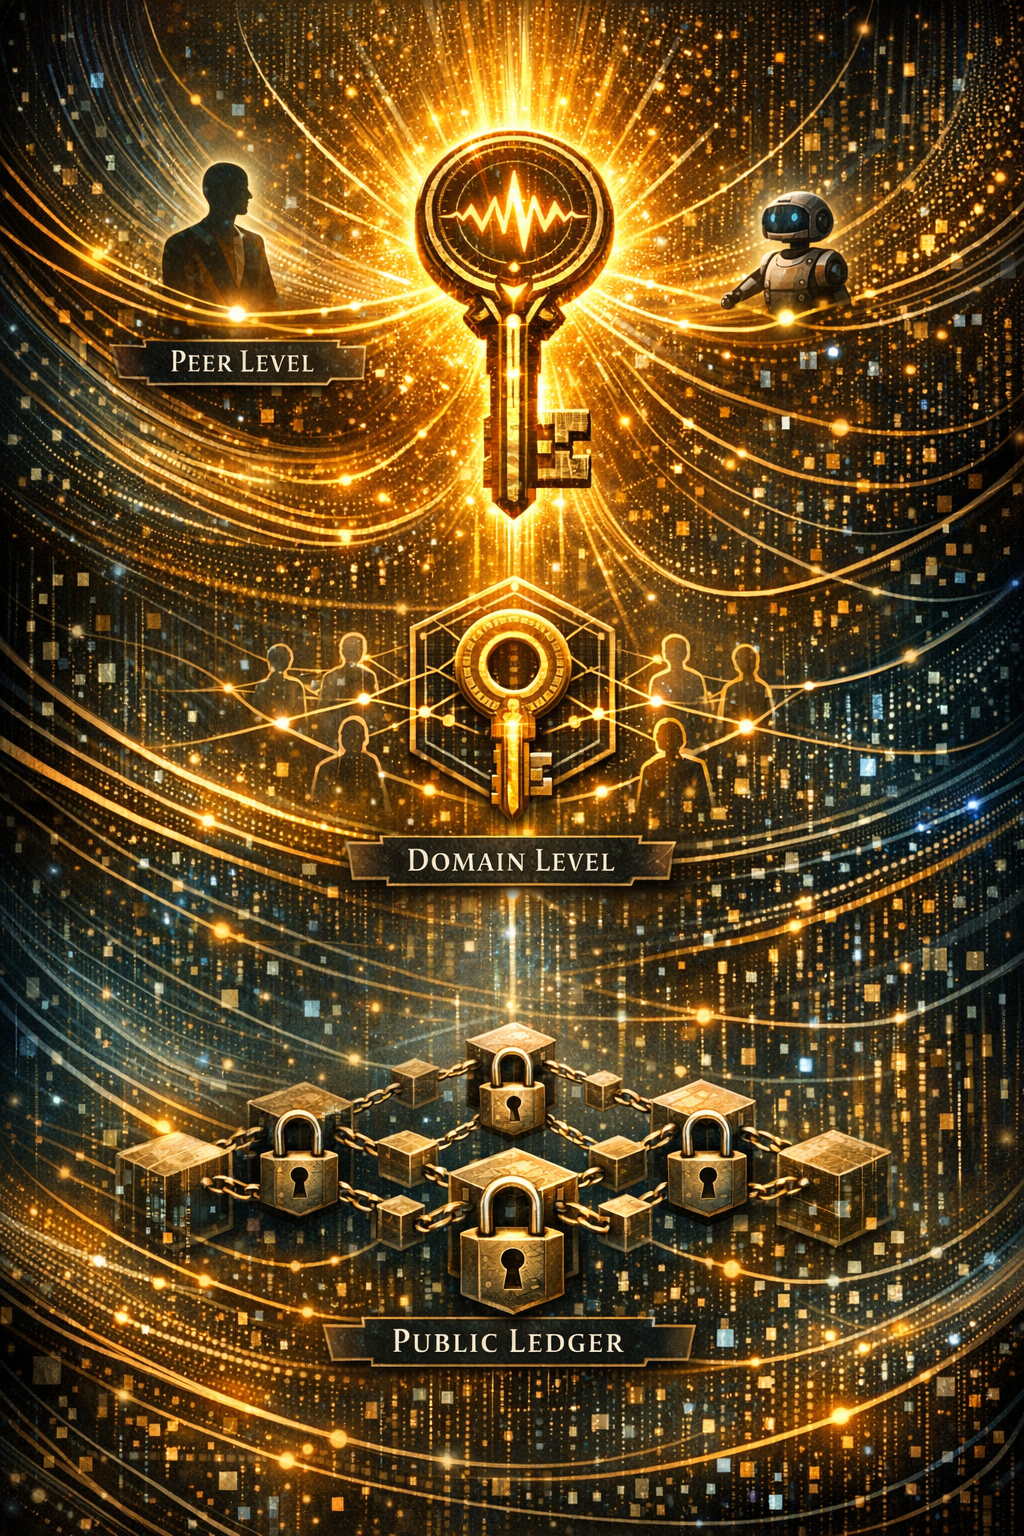
I've been experimenting with an additional credential that attempts to carry information about one of those other questions. I call it a tone key.
The name is provisional, and so is almost everything else.
Control and continuity
Suppose I've controlled the same cryptographic key for ten years. Yesterday I signed a transaction with it, and today I sign another. Cryptographically, the continuity is excellent: something controlled the same key both times.
A great deal about me could nevertheless have changed between those signatures. I could be acting under unusual pressure. Someone else could have obtained the key. My intentions could have changed completely. In an organization, the people represented by a long-lived organizational credential could have changed while the credential remained exactly the same.
That suggests there may be value in keeping another kind of evidence alongside control: information about the history immediately surrounding the use of the credential.
My earlier description went too far here. I said a tone key would prove, I am present. That's more than cryptography can establish from the proposed inputs. A more defensible claim would be that this credential was derived by a specified process from an interaction history that satisfied specified conditions.
That's less dramatic, but it's something we might actually be able to build.
Imagine a local system that maintains a rolling record of interaction with its owner. It measures a set of behavioral properties over time, derives a changing value from those measurements, and uses that value as one input to a cryptographic derivation process. The resulting credential doesn't prove that the person is coherent, sober, free from coercion, or metaphysically the same person they were yesterday. It proves something about the state of the measurement process.
Whether that state tells us anything useful about the person is an empirical question. That's where the project gets interesting.
Start with anomaly, not identity
Suppose I normally interact with a local agent in a way that produces a fairly stable collection of measurements. Then one day several of those measurements change abruptly. My pace changes, the structure of the exchange changes, previously stable interaction patterns disappear, and the way earlier information is carried forward changes.
That doesn't tell the system why. Maybe I'm under duress, drunk, sick, angry or simply in a hurry. Maybe someone else is using the interface. Maybe I've changed.
The measurement doesn't interpret itself. What it can potentially tell us is that the current interaction differs from the history against which it is being compared, and for a sufficiently consequential action that might justify another step. Perhaps that's a delay, another authentication factor, an explicit confirmation or an independent human check. The appropriate respons